



DHCP Spoofing là gì?
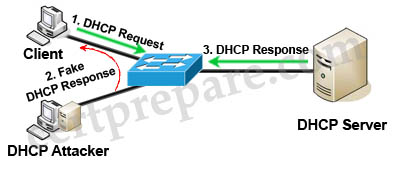
DHCP spoofing is a type of attack in that the attacker listens for DHCP Requests from clients and answers them with fake DHCP Response before the authorized DHCP Response comes to the clients. The fake DHCP Response often gives its IP address as the client default gateway -> all the traffic sent from the client will go through the attacker computer, the attacker becomes a “man-in-the-middle”.
The attacker can have some ways to make sure its fake DHCP Response arrives first. In fact, if the attacker is “closer” than the DHCP Server then he doesn’t need to do anything. Or he can DoS the DHCP Server so that it can’t send the DHCP Response.
DHCP snooping is a security feature that can prevent DHCP spoofing attacks. DHCP snooping is a Cisco Catalyst feature that determines which switch ports can respond to DHCP requests. Ports are identified as trusted and untrusted.
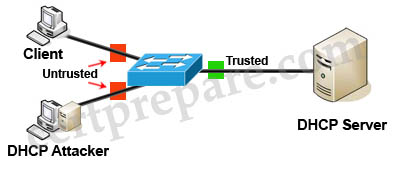
Only ports that connect to an authorized DHCP server are trusted, and allowed to send all types of DHCP messages. All other ports on the switch are untrusted and can send only DHCP requests. If a DHCP response is seen on an untrusted port, the port is shut down.
- BÌNH TĨNH TRƯỚC HỘP THƯ SỐ – NGHỆ THUẬT NHẬN DIỆN EMAIL PHISHING TỪ GÓC NHÌN NGHIỆP VỤ
- HÓA THÂN THÀNH "KẺ TẤN CÔNG": KHI HIỂU RÕ CẠM BẪY, TA PHÒNG THỦ VỮNG VÀNG HƠN
- CÁC CÔNG CỤ XÂY DỰNG GIAO DIỆN ỨNG DỤNG BẰNG TRÍ TUỆ NHÂN TẠO (AI)
- Silent Lynx khai thác lỗ hổng WinRAR để triển khai Reverse Shell nhằm tấn công các cơ quan chính phủ
- Thông tin xác thực ConnectWise bị chiếm dụng, 173 môi trường Microsoft 365 bị truy cập trái phép